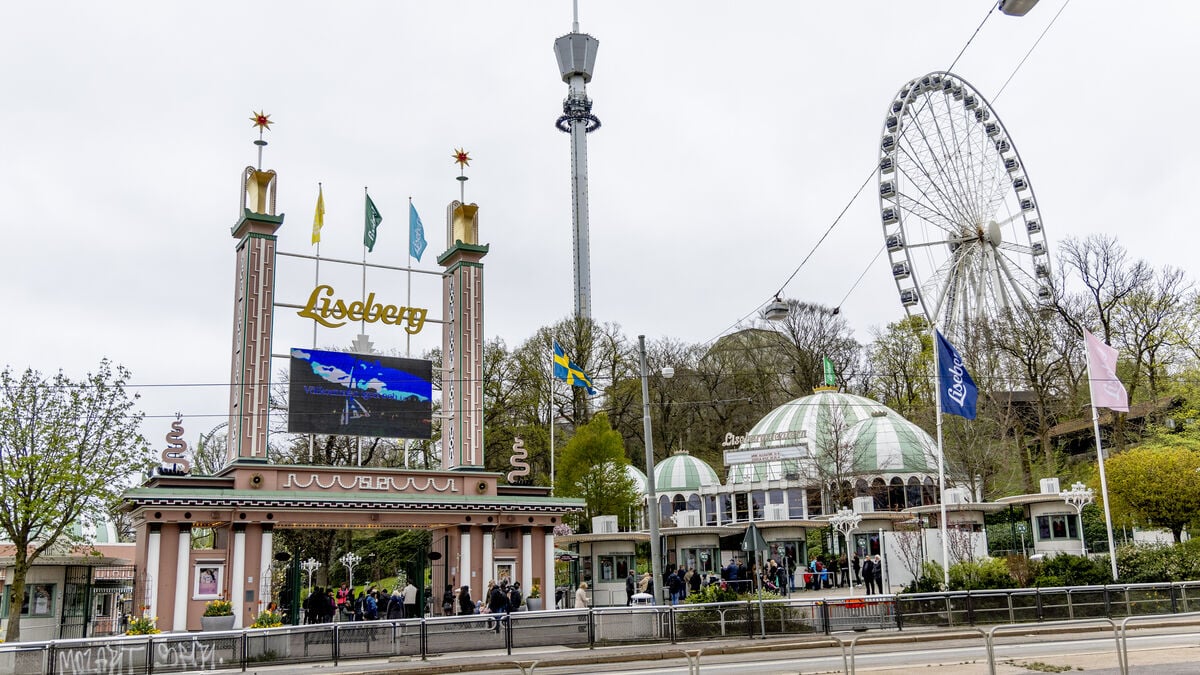
"We urge you to be extra careful with emails and text messages asking you to click on links, provide information or make a payment," Liseberg writes on its website.
Skansen tells Dagens Nyheter that unauthorized parties have gained access to information about people who booked tickets to the park between October 23 and 26. This follows a data breach at ticket provider Visit. Skansen is also warning of phishing.
According to Göteborgs-Posten, Liseberg also uses Visit.
We are in close dialogue and collaborating with the system supplier, which has taken measures, Liseberg communications manager Clara Rosendahl tells the newspaper.
No payment or card details were included in the breach at either Liseberg or Skansen. Skansen says that names, addresses, telephone numbers, email addresses and information about ticket purchases have been leaked.
It is unclear whether the incidents are related.
The reports come after vulnerabilities in the widely used programming language PHP were exposed. The flaws became known last week, prompting authorities and companies around the world to shut down their websites to avoid the risk of being hacked.